ASA packet tracer
ASA Packet Tracer is a network troubleshooting tool that
-
sends synthetic packets into the network to evaluate how existing routing configuration, NAT rules, and policy configurations affect that packet
-
works on live, online ASA devices either physical or virtual, and
-
evaluates packets based on the saved configuration on the ASA, not staged changes.
Troubleshooting use cases
Use this tool to troubleshoot these kinds of issues:
-
Users report that they cannot reach resources that they should be able to.
-
Users report that they can reach resources they should not be able to.
-
Test a policy to determine if it works as you expect.
Packet tracer can be used on a live, online, ASA device either physical or virtual. Packet Tracer does not work on ASA model devices. Packet tracer evaluates packets based on the saved configuration on the ASA. Staged changes on Security Cloud Control are not evaluated by packet tracer.
We consider it a best-practice to run packet tracer on an ASA that is in the synced state. Though packet tracer will run if the device is not synced, you could encounter some unexpected results. For example, if you deleted a rule in the staged configuration on Security Cloud Control, and this same rule was triggered on the ASA during packet tracing, Security Cloud Control won't be able to show you the result of the packet's interaction with that rule.
As packet tracer sends the packet through the routing configuration, NAT rules, and security policies of your ASA, it displays the packet's status at each step. If the packet is allowed by the policy it receives a green checkmark  . If a packet is denied and dropped, Security Cloud Control displays a red X
 .
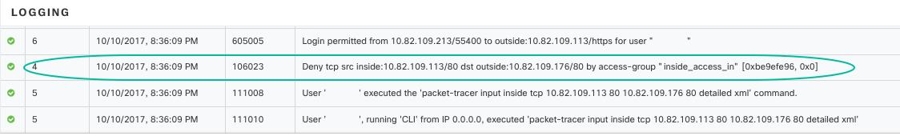
Packet tracer also displays a real time log of the result of the packet trace. In the example below, you can see where a rule denied a tcp packet.